A reported vulnerability in Coldcard’s key-generation process has prompted renewed scrutiny of single-device Bitcoin custody and increased interest in multisignature setups that spread signing authority across different hardware wallet manufacturers.
The issue, described as a Coldcard entropy bug or “Worm,” reportedly remained undiscovered since at least 2021. More than $100 million worth of Bitcoin was said to have been exposed, with most affected funds held in single-seed wallets. Casa CEO Nick Neuman said approximately 233,000 BTC moved to safer storage in response to the incident.
Why the incident challenged single-signature custody
Single-signature wallets depend on one device or software implementation to generate and protect the private key. If that process produces weak or predictable randomness, an attacker may be able to reconstruct the keys and spend the funds.
Coldcard users had little reason to distrust the manufacturer, given its established reputation. However, many appear to have relied solely on the entropy generated by the device without adding a passphrase or performing additional dice rolls. Those extra steps can contribute user-generated randomness to the key-creation process, but they were not part of every wallet setup.
The incident has also revived broader concerns about self-custody. Historical Bitcoin losses have frequently resulted from missing or damaged backups, forgotten passwords and weak security practices. Theft remains another major risk, including attacks involving malicious wallet software, compromised applications and social engineering.
How multi-vendor multisig changes the risk
Multisignature wallets use Bitcoin scripts that require a predetermined number of signatures before funds can be spent. A common arrangement is a 2-of-3 wallet, in which any two of three independent keys can authorize a transaction.
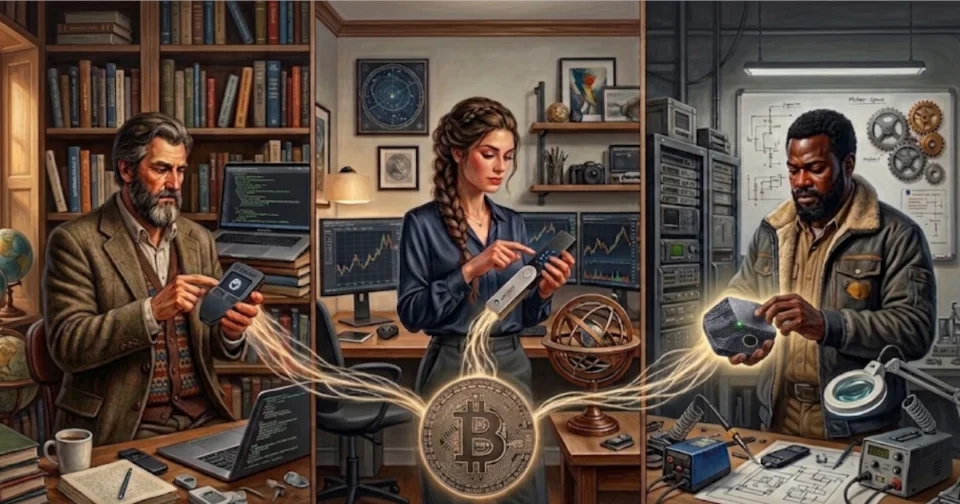
In a multi-vendor design, those keys are generated with products from different providers. For example, one key could be created with a Trezor Safe 7, another with a Ledger Nano device and a third held as a recovery key by a multisig provider. If one manufacturer suffers a key-generation or firmware failure, the compromised key alone should not be sufficient to move the Bitcoin.
More complex structures, including 3-of-5 wallets, can distribute control among additional devices or locations. Companies and software tools associated with Bitcoin multisig include Casa, Unchained Capital, Nunchuk and Sparrow. These services coordinate partially signed transactions, while the actual signing authority remains distributed among the participating keys.
Protection beyond hardware failures
Multisig can also reduce the impact of physical coercion and social-engineering attacks. Multi-jurisdictional arrangements may require the owner to reach different signers before a transaction can be completed. Time-locked recovery procedures can introduce an additional delay; in some designs, a recovery key may be unable to authorize a transaction for two weeks after a request is submitted.
These mechanisms are intended to make rapid unauthorized transfers more difficult, particularly in cases involving threats, phishing or pressure to approve a transaction. Multisig has also supported insurance products such as those offered by AnchorWatch, whose Bitcoin theft protection is provided through Lloyd’s of London for its current U.S. customers.
Multisig adds operational responsibility
Distributed custody is not risk-free. Owners must preserve the required threshold of keys and maintain accurate records of the wallet’s multisig script, sometimes called the wallet template or configuration. Without that information, recovering the funds can become difficult even when the underlying keys remain available.
Multisig providers may store this configuration for users and, in some cases, offer company-managed recovery keys. Other tools, including Sparrow and Nunchuk, are designed to give users greater control over the recovery process, although Nunchuk also offers a paid recovery-key service.
The Coldcard incident has therefore not eliminated the need for careful security planning. Instead, it has highlighted the trade-off between convenience and resilience: multi-vendor multisig requires more preparation, but it can reduce dependence on any single hardware wallet maker or key-generation process.
